Subject: Potential Udon Security Bypass - Player Username Exfiltration Through Sequential URL Requests
1. What Is the Vulnerability?
I am reporting a potential security vulnerability involving the transmission of VRChat player usernames to external servers through sequential, predefined URL requests.
The reported implementation is associated with the VRChat world Popcorn Palace.
Affected World:
- Name: Popcorn Palace
- World ID:
wrld_266523e8-9161-40da-acd0-6bd82e075833- URL: https://vrchat.com/home/world/wrld_266523e8-9161-40da-acd0-6bd82e075833/info
### Technical Overview
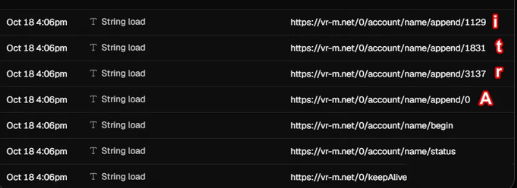
The implementation reportedly uses a sequence of URL requests to transmit a player's username one character at a time.
The process appears to operate as follows:
1. START Request: An initial request signals the beginning of a data transmission.
2. LETTER Requests: Individual predefined URL requests represent characters of the player's username. These are submitted sequentially through scripting.
3. CLOSE Request: A final request signals that the transmission is complete, allowing the external receiving server to reconstruct the original username.
Rather than constructing a single dynamic URL containing player information, this technique appears to encode dynamic information through the order and selection of predefined URL requests.
The concern is that this creates a functional data transmission channel through an interface that may have been intentionally restricted from transmitting arbitrary dynamic information.
### Potential Security Boundary Bypass
VRChat's SDK License includes restrictions concerning the external transmission of user information and dynamic data.
Sections 4.1 and 4.2 are particularly relevant to determining whether this behavior is authorized.
If the described mechanism is accurate, it may effectively bypass the intended restrictions on transmitting player information to external services.
I have not independently verified the complete implementation, the receiving server's behavior, or whether the creator has received authorization from VRChat.
I am requesting that VRChat investigate whether this is an intended capability, an authorized exception, or an unintended circumvention of the platform's security restrictions.
---
2. Steps to Reproduce
The following steps describe how the reported behavior could be investigated. They are not presented as an independently verified reproduction.
Affected World:
https://vrchat.com/home/world/wrld_266523e8-9161-40da-acd0-6bd82e075833/info
1. Launch VRChat and enter the Popcorn Palace world.
2. Determine whether the world contains scripted functionality that initiates external URL requests associated with player identification.
3. Observe whether a START request initiates a sequence of external requests.
4. Examine whether subsequent requests correspond to individual characters of a player's username.
5. Determine whether the sequence concludes with a CLOSE request.
6. Investigate whether the receiving server reconstructs the username from the ordered sequence.
7. Determine whether the transmission requires explicit player interaction or consent, and whether it uses a VRChat-authorized external data mechanism.
### Expected Security Behavior
External URL functionality should operate within VRChat's intended security restrictions, including any applicable limitations on transmitting dynamic player information to external servers.
### Reported Behavior
A sequence of predefined URL requests may allow dynamic player information to be encoded and reconstructed externally, despite restrictions on constructing arbitrary dynamic URLs.
### Reproduction Limitations
I have not supplied an independently verified network trace or controlled proof-of-concept demonstrating this mechanism.
VRChat's internal review of the affected world's implementation may be necessary to establish the precise behavior and determine whether it constitutes a security vulnerability.
---
3. Potential Impact
If this technique operates as reported and bypasses an intended security restriction, the implications extend beyond the transmission of usernames.
### 1. External Player Identification
World creators could potentially transmit player usernames to external databases and associate them with persistent records.
This would allow external systems to recognize returning players and maintain information about their activity.
### 2. Persistent Player Tracking
An external service could potentially record when particular players visit participating worlds, associate visits with timestamps, and build historical activity records.
The extent of this capability would depend on the information accessible through Udon and the conditions under which the requests are triggered.
### 3. Circumvention of Dynamic Data Restrictions
The underlying technique may be applicable to information other than usernames.
If arbitrary information can be represented through sequences of predefined requests, the same mechanism could potentially transmit other dynamic values available to world scripting.
This raises the possibility of a broader communication channel operating outside VRChat's intended restrictions.
### 4. Privacy and Consent Concerns
If player information is transmitted without meaningful disclosure or consent, users may be unaware that their identifiers are being collected by external systems.
The security implications depend on the information collected, how it is stored, and whether users have authorized the transmission.
### 5. Legitimate Development Applications
I also want to emphasize that the underlying functionality has legitimate value.
Persistent player identifiers could enable:
- Game progression across sessions.
- Persistent achievements and player statistics.
- External leaderboards.
- World analytics and player retention metrics.
- Persistent gameplay data linked to individual users.
I have personally wanted access to this functionality for years as a VRChat world developer.
The issue is not that persistent player identification is inherently malicious.
The issue is whether this particular implementation circumvents an intentional security restriction and, if so, whether the platform provides appropriate controls for its use.
### Potential Scope
If the technique is reproducible using generally available Udon functionality, other world creators may be able to implement similar systems.
The potential impact is therefore not necessarily limited to the identified world.
I am not claiming that the identified creator has used this technique maliciously. I am reporting the potential security implications of the underlying mechanism.
---
4. Description and Request for Clarification
Hello VRChat Security Team,
I am submitting this report in good faith regarding a potentially unintended method of transmitting player information from VRChat worlds to external servers.
The reported implementation is associated with Popcorn Palace.
Affected World:
- Name: Popcorn Palace
- World ID:
wrld_266523e8-9161-40da-acd0-6bd82e075833- URL: https://vrchat.com/home/world/wrld_266523e8-9161-40da-acd0-6bd82e075833/info
### Background
For years, I have been interested in obtaining some form of persistent, unique player identifier within VRChat worlds.
The ability to associate individual players with external databases would make it possible to build significantly more advanced persistent gameplay systems, statistics, achievements, and other features.
However, VRChat's restrictions on dynamic external data transmission have historically limited how these systems can be implemented.
The reported Popcorn Palace implementation appears to have discovered a clever workaround.
By submitting a START request, transmitting individual characters through predefined URL requests, and then submitting a CLOSE request, the system reportedly allows an external server to reconstruct a player's username.
From a technical standpoint, I find this interesting.
It appears to accomplish something I have wanted to do for a considerable amount of time.
However, I am concerned that the mechanism may circumvent security restrictions VRChat intentionally established.
### Relevant Policy
VRChat's SDK License, particularly Sections 4.1 and 4.2, contains restrictions concerning external data transmission and the use of internet-connected components to send dynamic information outside the platform.
Official Reference:
https://hello.vrchat.com/legal/sdk
I am requesting clarification about whether this technique is compatible with those restrictions.
### Questions for the Security Team
1. Is transmitting dynamic player information through sequences of predefined URL requests an intended and supported capability of Udon?
2. Does encoding information into the selection and order of otherwise permitted requests circumvent the intended restrictions on dynamic external data transmission?
3. Is the reported implementation considered a security vulnerability, a permitted technical workaround, or functionality that requires explicit authorization?
4. If this technique is permitted, can other world creators implement equivalent systems for persistent game data, player statistics, and external database integration?
5. If it is not permitted, is VRChat considering an officially supported alternative for persistent player identification and external data association?
### My Position
I am not submitting this report to demand moderation action against the creator of Popcorn Palace.
I recognize the technical creativity involved, and I am genuinely interested in the functionality it makes possible.
At the same time, I believe it is important for VRChat to establish whether this is an acceptable implementation.
If the platform permits this method, world creators should be able to understand and use it within clearly defined guidelines.
If the method circumvents an intentional security boundary, the vulnerability should be evaluated and addressed appropriately.
My goal is to understand the technical and policy boundaries so that creators can build more advanced experiences without inadvertently violating VRChat's rules.
### Public Reference
I have also raised the question publicly:
https://x.com/Engineerisaac/status/2112226247069868384
This report is intended to provide a formal technical disclosure and request for investigation, not a user moderation complaint.
Thank you for reviewing the report.
Engineerisaac
Side Note: Its showing in threads others have been bonked for this
Comments